Skip to content

SSO, SCIM, RBAC and audit log for a private AI assistant

DocsGPT signs people in through your identity provider with OIDC SSO, provisions them with SCIM 2.0, and controls access with roles, teams and sharing. Admins see every sign-in and change in one Activity feed they can export, cap spend with usage quotas, and trace every run into the monitoring they already use.

oidc sso · scim 2.0 · roles · activity · quotas · traces

Last updated: · Facts checked on

app.docsgpt.cloud — Admin

Single sign-on and SCIM provisioning

Sign in through your identity provider, and let your directory add and remove people.

DocsGPT signs people in through your identity provider over OpenID Connect, with documented setups for Microsoft Entra ID, Okta, Keycloak and Authentik, and works with any OIDC provider that publishes a discovery document.

Group allowlists decide who may sign in and admin groups decide who administers; both are re-checked at every session renewal, so removing someone from a group cuts their access promptly. SCIM 2.0 creates, deactivates and reactivates accounts from your directory, and back-channel logout ends sessions when your IdP says so.

oidc · pkce · group allowlist · admin groups · scim 2.0 · back-channel logout

Identity providers
 ProtocolSupport
Microsoft Entra IDOIDCDocumented setup
OktaOIDC · SCIMWorks with the default web-app configuration; SCIM connector documented
KeycloakOIDCDocumented setup, group mapping, back-channel logout
AuthentikOIDC · SCIMReference setup in the docs, including SCIM
Any OIDC providerOIDCAny provider with a discovery document
  1. 01

    Assign the app in your directory

    SCIM creates the account before the first sign-in, so nobody has to be set up by hand.

  2. 02

    People sign in with SSO

    Group allowlists decide who may sign in and admin groups decide who administers, re-checked at every session renewal.

  3. 03

    Leavers lose access at once

    Deactivating someone in your directory revokes their sessions immediately; reactivating restores access.

Roles, teams and sharing

Roles are enforced on the server on every request, never trusted from the browser. An instance admin runs the console; inside a team, team admins manage membership and members use what is shared with them. Teams are self-serve.

The first admin is granted from the command line or from an IdP group, and the console refuses to remove the last one.

admin · user · team admin · team member

Instance and team roles
 ScopeCan
UserInstanceUse DocsGPT and own their agents, knowledge, prompts and tools
AdminInstanceEverything a user can, plus users, admins, usage, quotas, connectors and Activity
Team adminTeamManage the team's members and settings; not an instance admin
Team memberTeamUse what is shared with the team

Sharing

Viewer or Editor, per resource

Share agents, knowledge, prompts and tools with a team or one person. Viewers use them; editors change them. Owners decide whether editors may share or delete, and whether viewers can see an agent's logs.

viewer · editor · editors can share · viewers can see logs
Shared agents

Agents that keep working

An agent shows what it uses and whose access each item runs with. When an editor adds a tool or source, it runs with their access, and the agent says when someone's access lapses.

what this agent uses · run with my access

Admin console

Users, tokens and connectors

Activate or deactivate accounts, grant admins, force a logout that also revokes the person's access tokens, and decide which connectors members may use.

users · admins · access tokens · connectors

One Activity feed, ready to export

Every sign-in, change and guardrail decision in one append-only timeline.

Admin › Activity brings sign-ins and denials, provisioning, role and account changes, access tokens, quota and connector-policy changes, data changes, remote-device commands and guardrail decisions into one timeline. Every row records who acted and who was affected.

Filter by category, event, person or time window, search inside the details, and export exactly what you filtered as CSV or NDJSON for your SIEM or an access review. Per-agent Guardrail activity and conversation logs with feedback sit alongside it.

Activity

Categories
identity · access · config · data · device · safety
Filters
category · event · actor · affected user · time
Export
csv · ndjson
Journal
append-only

Usage, quotas and cost

See who spends what, and cap it before the invoice does.

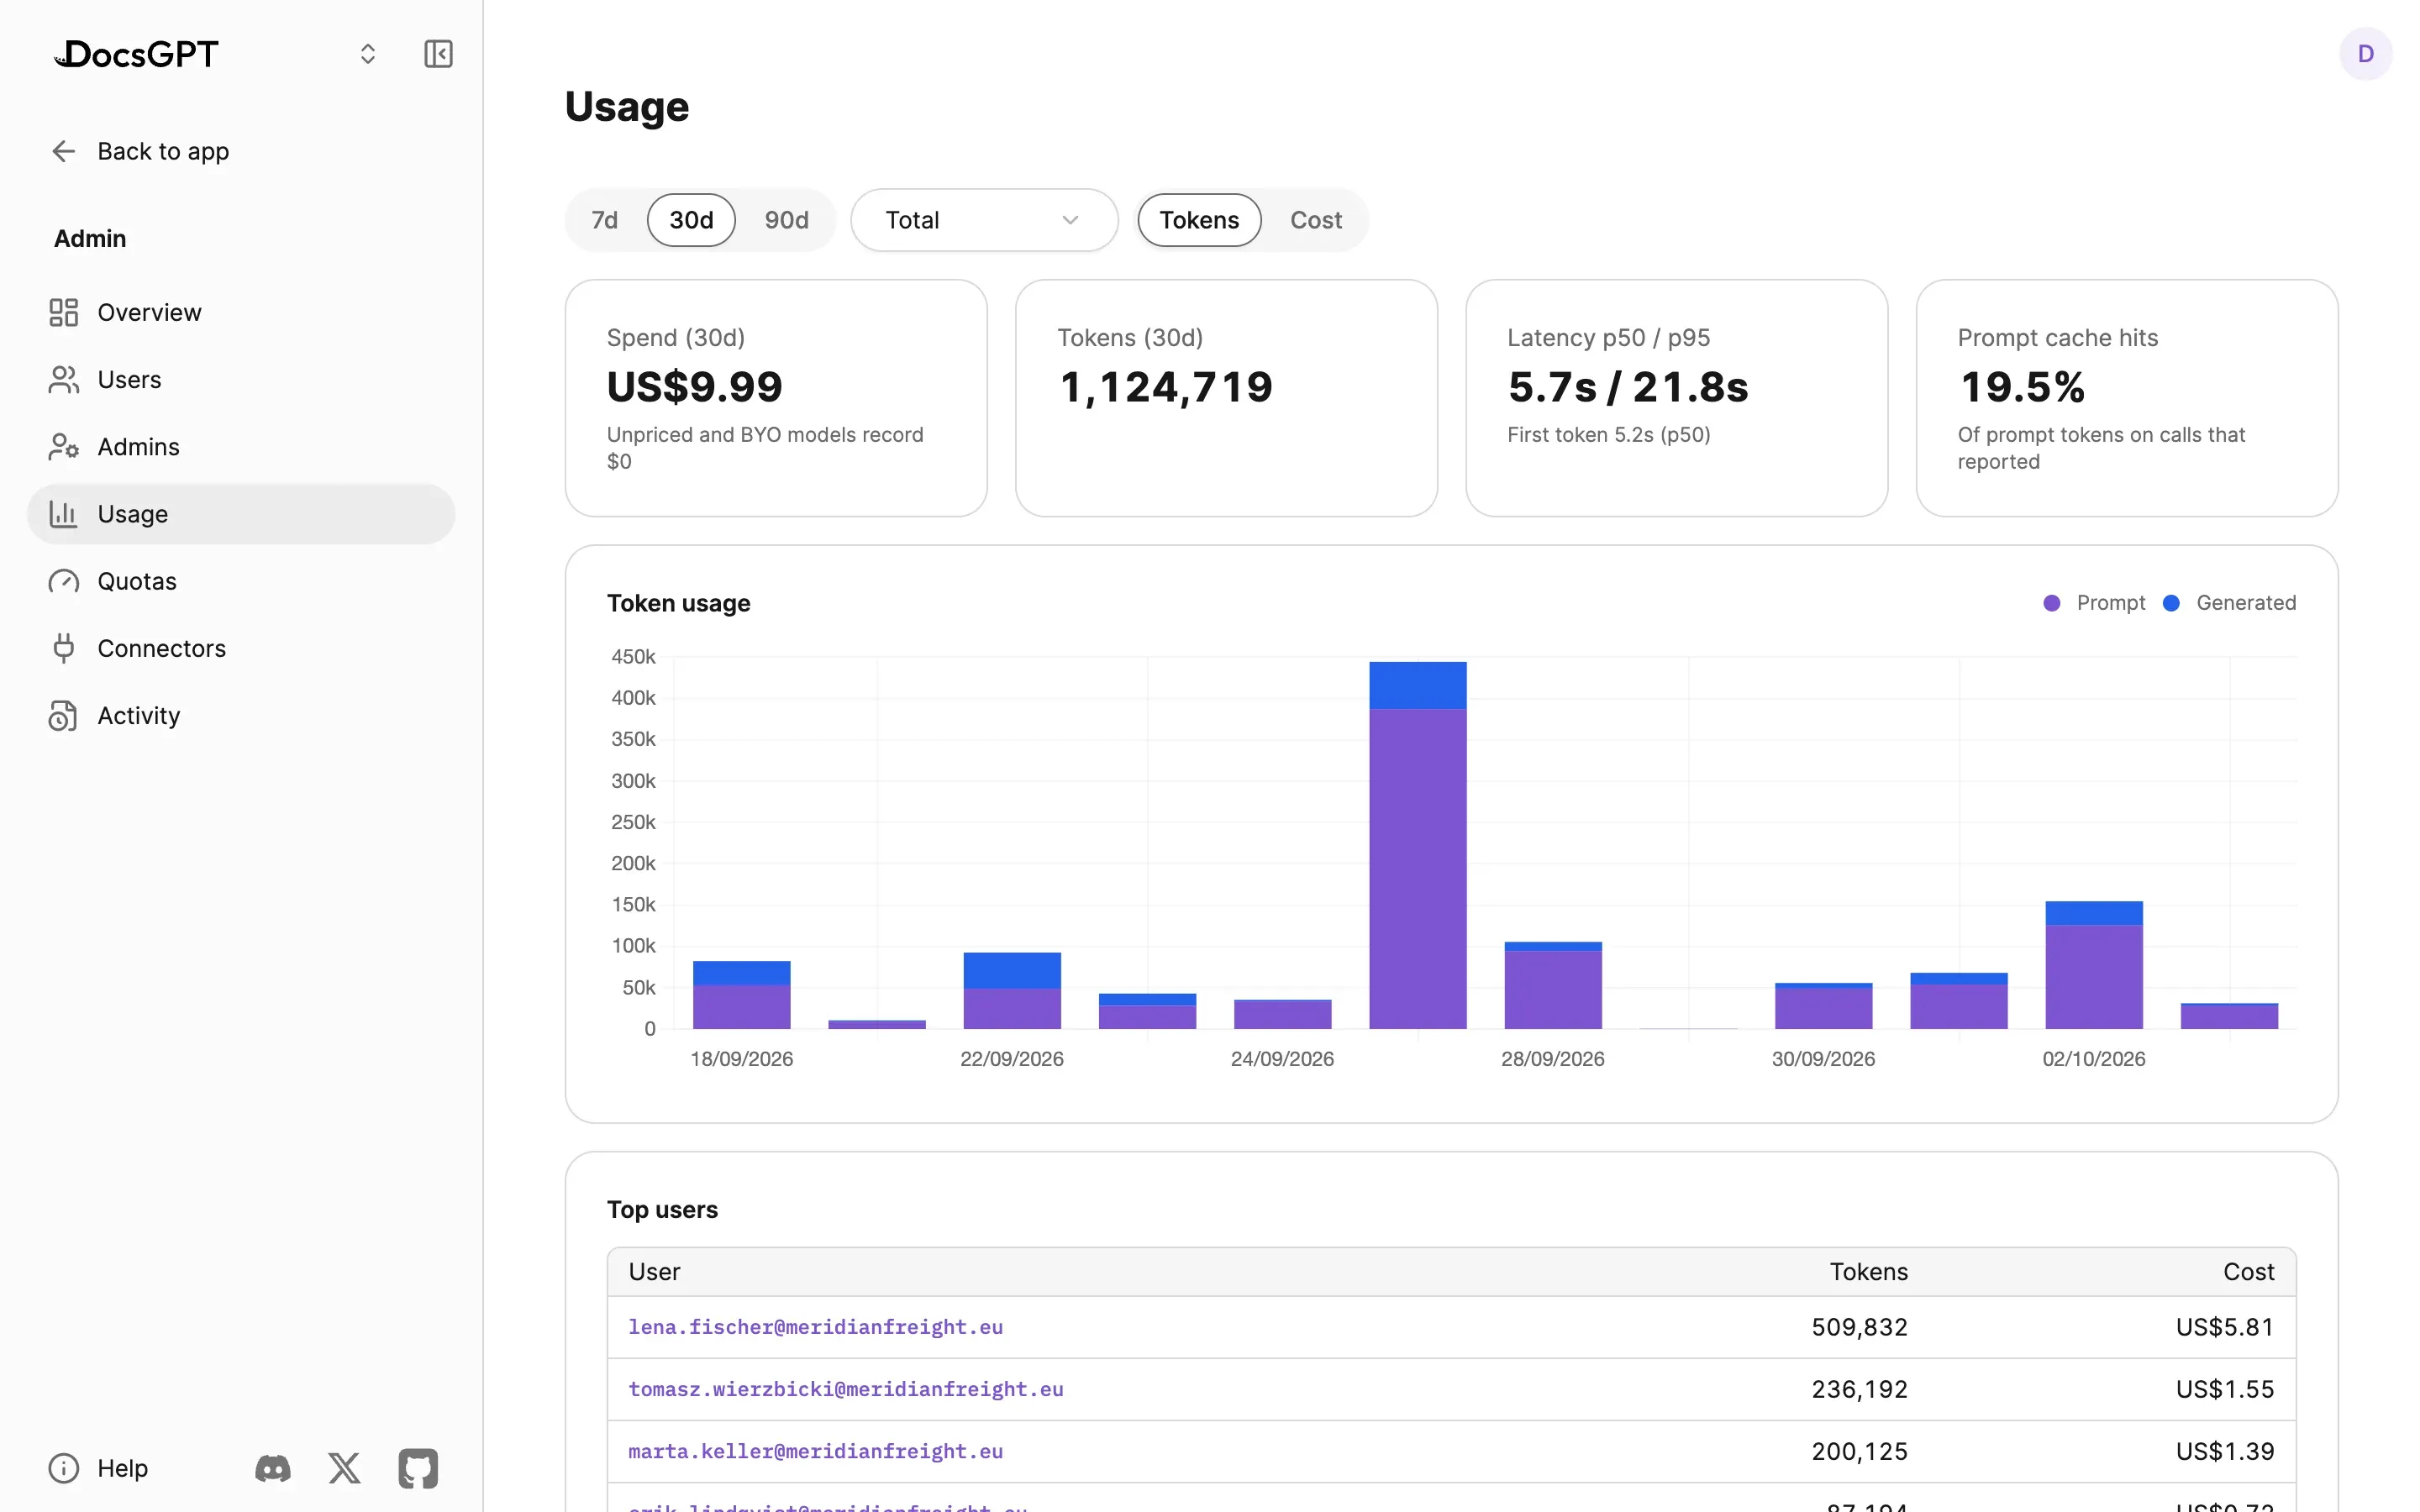
Admin › Usage shows spend and tokens over time, latency at the median and the 95th percentile, prompt-cache hits and the top users, split by model, agent or flow.

Usage quotas cap tokens, spend or both per user per day, week or month. Set an instance default, give a team a per-member allowance, and override it for one person; a request over the limit is refused.

spend · tokens · p50 / p95 · by model, agent or flow · quotas

app.docsgpt.cloud — Admin › Usage
Admin › Usage over 30 days: spend, tokens, latency p50 and p95 and prompt-cache hits, a token-usage chart split into prompt and generated tokens, and a table of top users by tokens and cost.
app.docsgpt.cloud — Admin › Usage
Admin › Usage over 30 days: spend, tokens, latency p50 and p95 and prompt-cache hits, a token-usage chart split into prompt and generated tokens, and a table of top users by tokens and cost.

Execution traces and observability

Every run leaves a trace you can open, or send to the tools you already use.

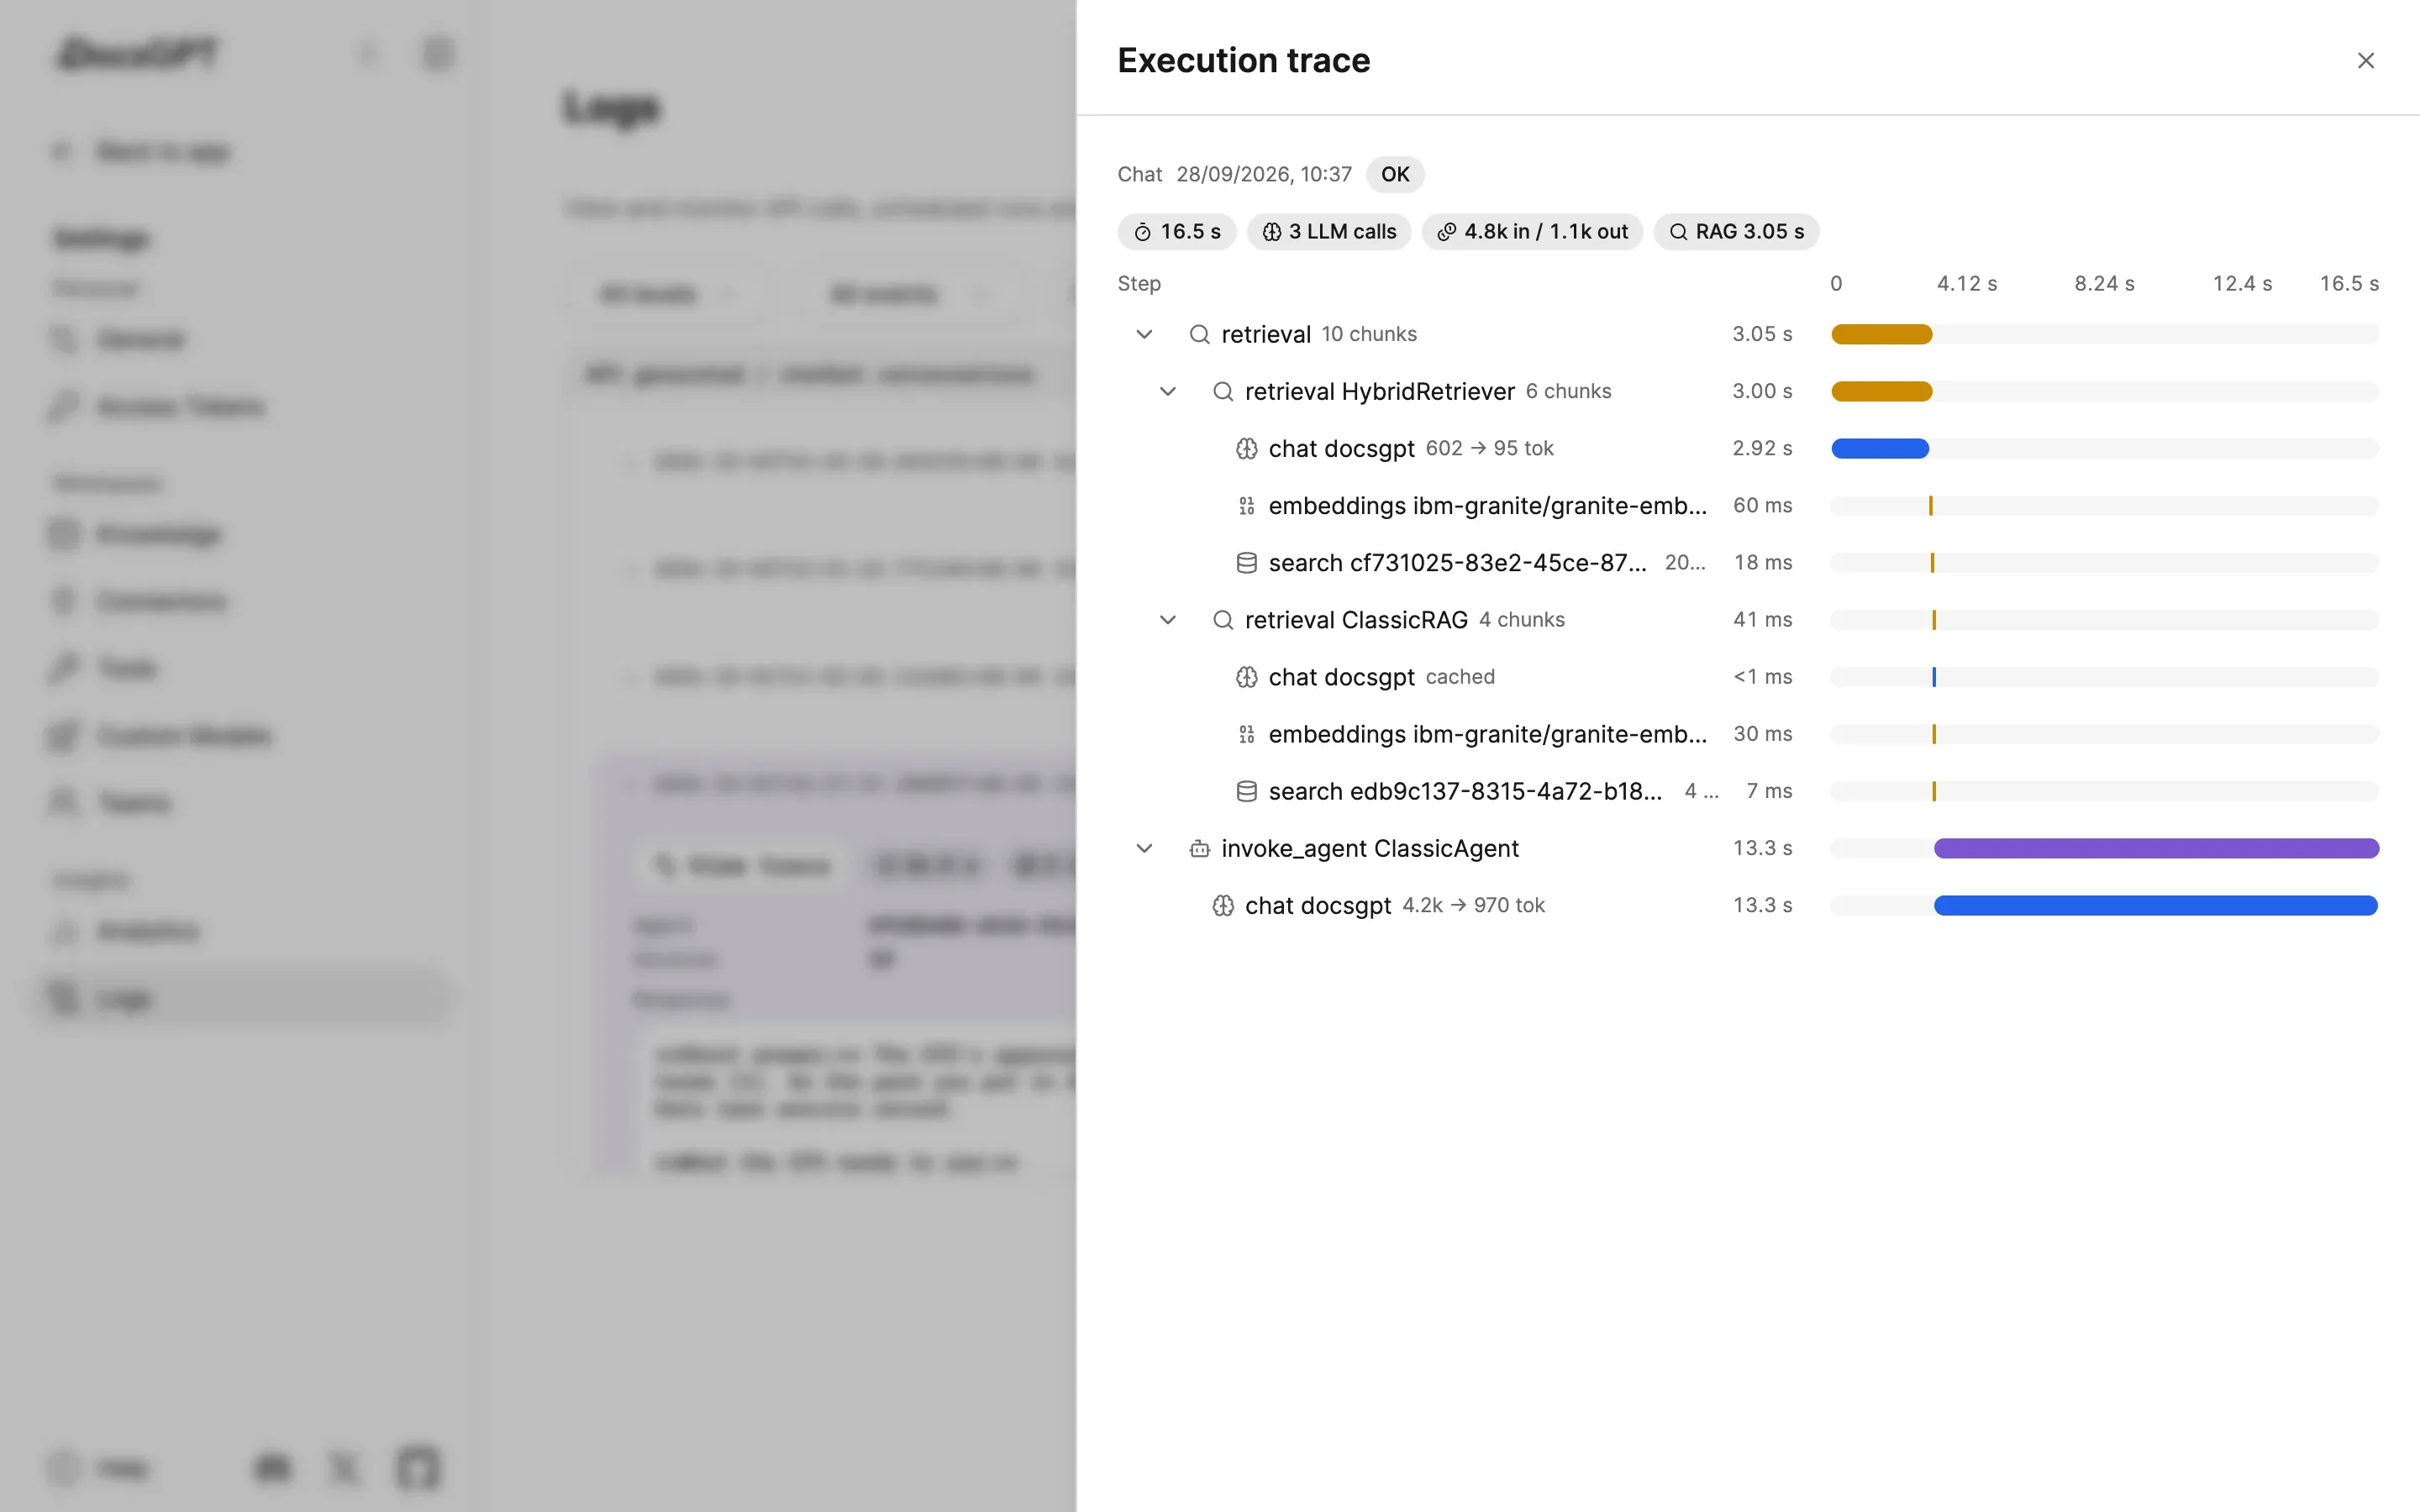
Logs keep every chat, workflow, schedule, webhook, search and graph build. Open a trace to see each step as a waterfall: retrieval, embeddings and searches, LLM calls with their tokens, tools, guardrails and workflow steps, each with its timing.

Traces export as OpenTelemetry GenAI spans to Langfuse, Arize Phoenix, Datadog LLM Observability or Grafana, and the service's own traces, metrics and logs go to any OpenTelemetry backend you run.

execution trace · otel genai spans · langfuse · phoenix · datadog · grafana

app.docsgpt.cloud — Logs › Execution trace
An execution trace for one chat answer: totals for duration, LLM calls, tokens and retrieval time, then a waterfall of steps — hybrid and classic retrieval with their embeddings and searches, and the agent's model call — each with its duration.
app.docsgpt.cloud — Logs › Execution trace
An execution trace for one chat answer: totals for duration, LLM calls, tokens and retrieval time, then a waterfall of steps — hybrid and classic retrieval with their embeddings and searches, and the agent's model call — each with its duration.

Security programme

Credentials

Encrypted credentials

Connector and tool credentials are encrypted on the server, the key can be rotated, and shared tools run without exposing them. On your own deployment, the key is yours.

encrypted · key rotation

Supply chain

SBOM and Dependabot

A software bill of materials is available for every release; dependencies are watched by Dependabot.

SBOM · Dependabot

CI

Static analysis and secret scanning

CodeQL, Bandit and zizmor run in CI; secret scanning guards the repository.

CodeQL · Bandit · zizmor

Disclosure

Coordinated disclosure

Private vulnerability reporting per SECURITY.md, with published advisories.

SECURITY.md

Hardening

Security checklist

A step-by-step checklist for going live: who can reach it, sign-in, secrets, HTTPS, outbound access and the audit trail.

security checklist

The full programme, the disclosure process and certification status are on Security.

How it runs privately

Identity stays with your IdP; DocsGPT never stores passwords for SSO users. Roles, teams, the Activity feed, usage and traces live in your own database, and telemetry goes only to the collector you configure, never to Arc53. On on-premises and air-gapped deployments the IdP is inside your network too; on Cloud, Arc53 operates the database.

SSO, SCIM, teams, sharing, the Activity feed and quotas are part of the platform in every deployment posture, self-hosted community builds included. See pricing for what else differs.

Example

A specialist consultancy on a dedicated instance with SSO.

Before moving 5,000+ documents onto a dedicated managed instance, a specialist consultancy asked three things: who can sign in, who administers, and what it costs per month.

The same platform and the same settings, operated by Arc53 on a single-tenant server.

Managed instance →

5,000+ documents · flat monthly fee

Dedicated managed instance for a specialist consultancy: 5,000+ documents, SSO, one flat monthly fee with no per-seat licence.

Source: No Deviation

Frequently asked questions

Does DocsGPT support SSO?

Yes. DocsGPT signs people in through any OpenID Connect provider with a discovery document, with documented setups for Microsoft Entra ID, Okta, Keycloak and Authentik. Group-based sign-in, admin groups, silent renewal and back-channel logout are included.

What is SCIM provisioning?

SCIM is the standard by which your directory creates, deactivates and reactivates accounts in an application. With SCIM 2.0 turned on, people get a DocsGPT account when they are assigned the app and lose access the moment they are deactivated, with every change in the Activity feed.

Is there an audit log for AI use?

Yes. Admin › Activity is one append-only timeline of sign-ins, provisioning, role and account changes, access tokens, quota and connector-policy changes, data changes, device commands and guardrail decisions. Filter it by category, person or time and export it as CSV or NDJSON.

Can I see and cap AI spend?

Yes. Admin › Usage shows spend, tokens, latency and top users, split by model, agent or flow. Usage quotas cap tokens or spend per user per day, week or month, with team allowances and an instance default; a request over the limit is refused.

Can I plug it into Grafana, Datadog or Langfuse?

Yes. Every run's trace can be exported as OpenTelemetry GenAI spans to Langfuse, Arize Phoenix, Datadog LLM Observability or Grafana, and the service's traces, metrics and logs go to any OpenTelemetry backend you run.

See DocsGPT on your documents

A 30-minute demo of SSO, SCIM, Activity and quotas, or a free on-premises review of your identity setup with an engineer.