OIDC SSO
Any spec-compliant IdP; Okta, Keycloak, Authentik and Entra ID documented. Authorization Code + PKCE; Back-Channel Logout.
group allowlists · admin group mapping
DocsGPT security rests on where you run it: on-premises and air-gapped deployments keep documents, prompts and models inside your network, with OIDC SSO, SCIM 2.0, role-based access, an exportable audit log and guardrails with human approval. The code is MIT-licensed with a public threat model, SBOM and CodeQL scanning; vulnerabilities are reported privately via GitHub.
MIT · public threat model · SBOM · CodeQL · SECURITY.md ↗
Last updated: · Facts checked on
Air-gapped means zero external network: local LLM, local embeddings, a self-hosted vector store and local file storage, or your own S3-compatible store if you prefer one. Hybrid is an on-premises platform with a cloud LLM of your choice; it is not air-gapped.
Cloud and Managed are operated by Arc53 under a 99.9 % uptime SLA with daily backups and point-in-time recovery; On-premises and Air-gapped are operated by the customer inside their own network. Only Air-gapped has no external egress at all.
| Cloud | Managed | On-premises | Air-gapped | |
|---|---|---|---|---|
| Data location | Arc53 cloud, EU region | Dedicated instance in the Americas, Europe, Middle East, Africa or Asia | Your data centre or private cloud | Your network |
| LLM location | Cloud provider via Arc53 | Cloud provider via Arc53, a local engine on the instance, or your own provider key (BYOM) | Local engine, or your cloud LLM (hybrid) | Local engine only |
| Network egress | Yes: LLM provider | Yes: LLM provider | Optional (hybrid only) | None |
| Who holds encryption keys | Arc53 and its hosting provider; no customer-managed keys | Arc53 and its hosting provider; customer-managed keys per contract | Customer | Customer |
| Who operates | Arc53, multi-tenant | Arc53, dedicated instance | Customer, with Arc53 support | Customer, with Arc53 support |
| Uptime SLA | 99.9 % uptime | 99.9 % uptime | Per contract | Per contract |
| Backups and recovery | daily · point-in-time recovery | daily · point-in-time recovery | Your platform, or per contract | Your platform, or per contract |
| Identity | OIDC SSO, SCIM 2.0 | OIDC SSO, SCIM 2.0 | OIDC SSO (Okta, Keycloak, Authentik, Entra ID), SCIM 2.0 | OIDC SSO, SCIM 2.0 against your internal IdP |
| Vendor access to content | Yes (Arc53 service processes content) | Yes (Arc53 operates the dedicated instance) | No | No |
| Customer data used to train models | No | No | No | No |
Hybrid = on-premises platform + cloud LLM; not air-gapped.
Cloud: your browser talks across the network boundary to DocsGPT and its vector store in the Arc53 cloud; DocsGPT calls an LLM provider. Managed: the same flow, but DocsGPT and the vector store run on a dedicated instance in your chosen region. On-premises: browser, DocsGPT, vector store and a local LLM all run inside your network; optionally (hybrid) DocsGPT sends prompts to a cloud LLM you choose, which is the only boundary crossing. Air-gapped: browser, DocsGPT, local LLM, local embeddings, vector store and file storage all run inside your network with no external network at all.
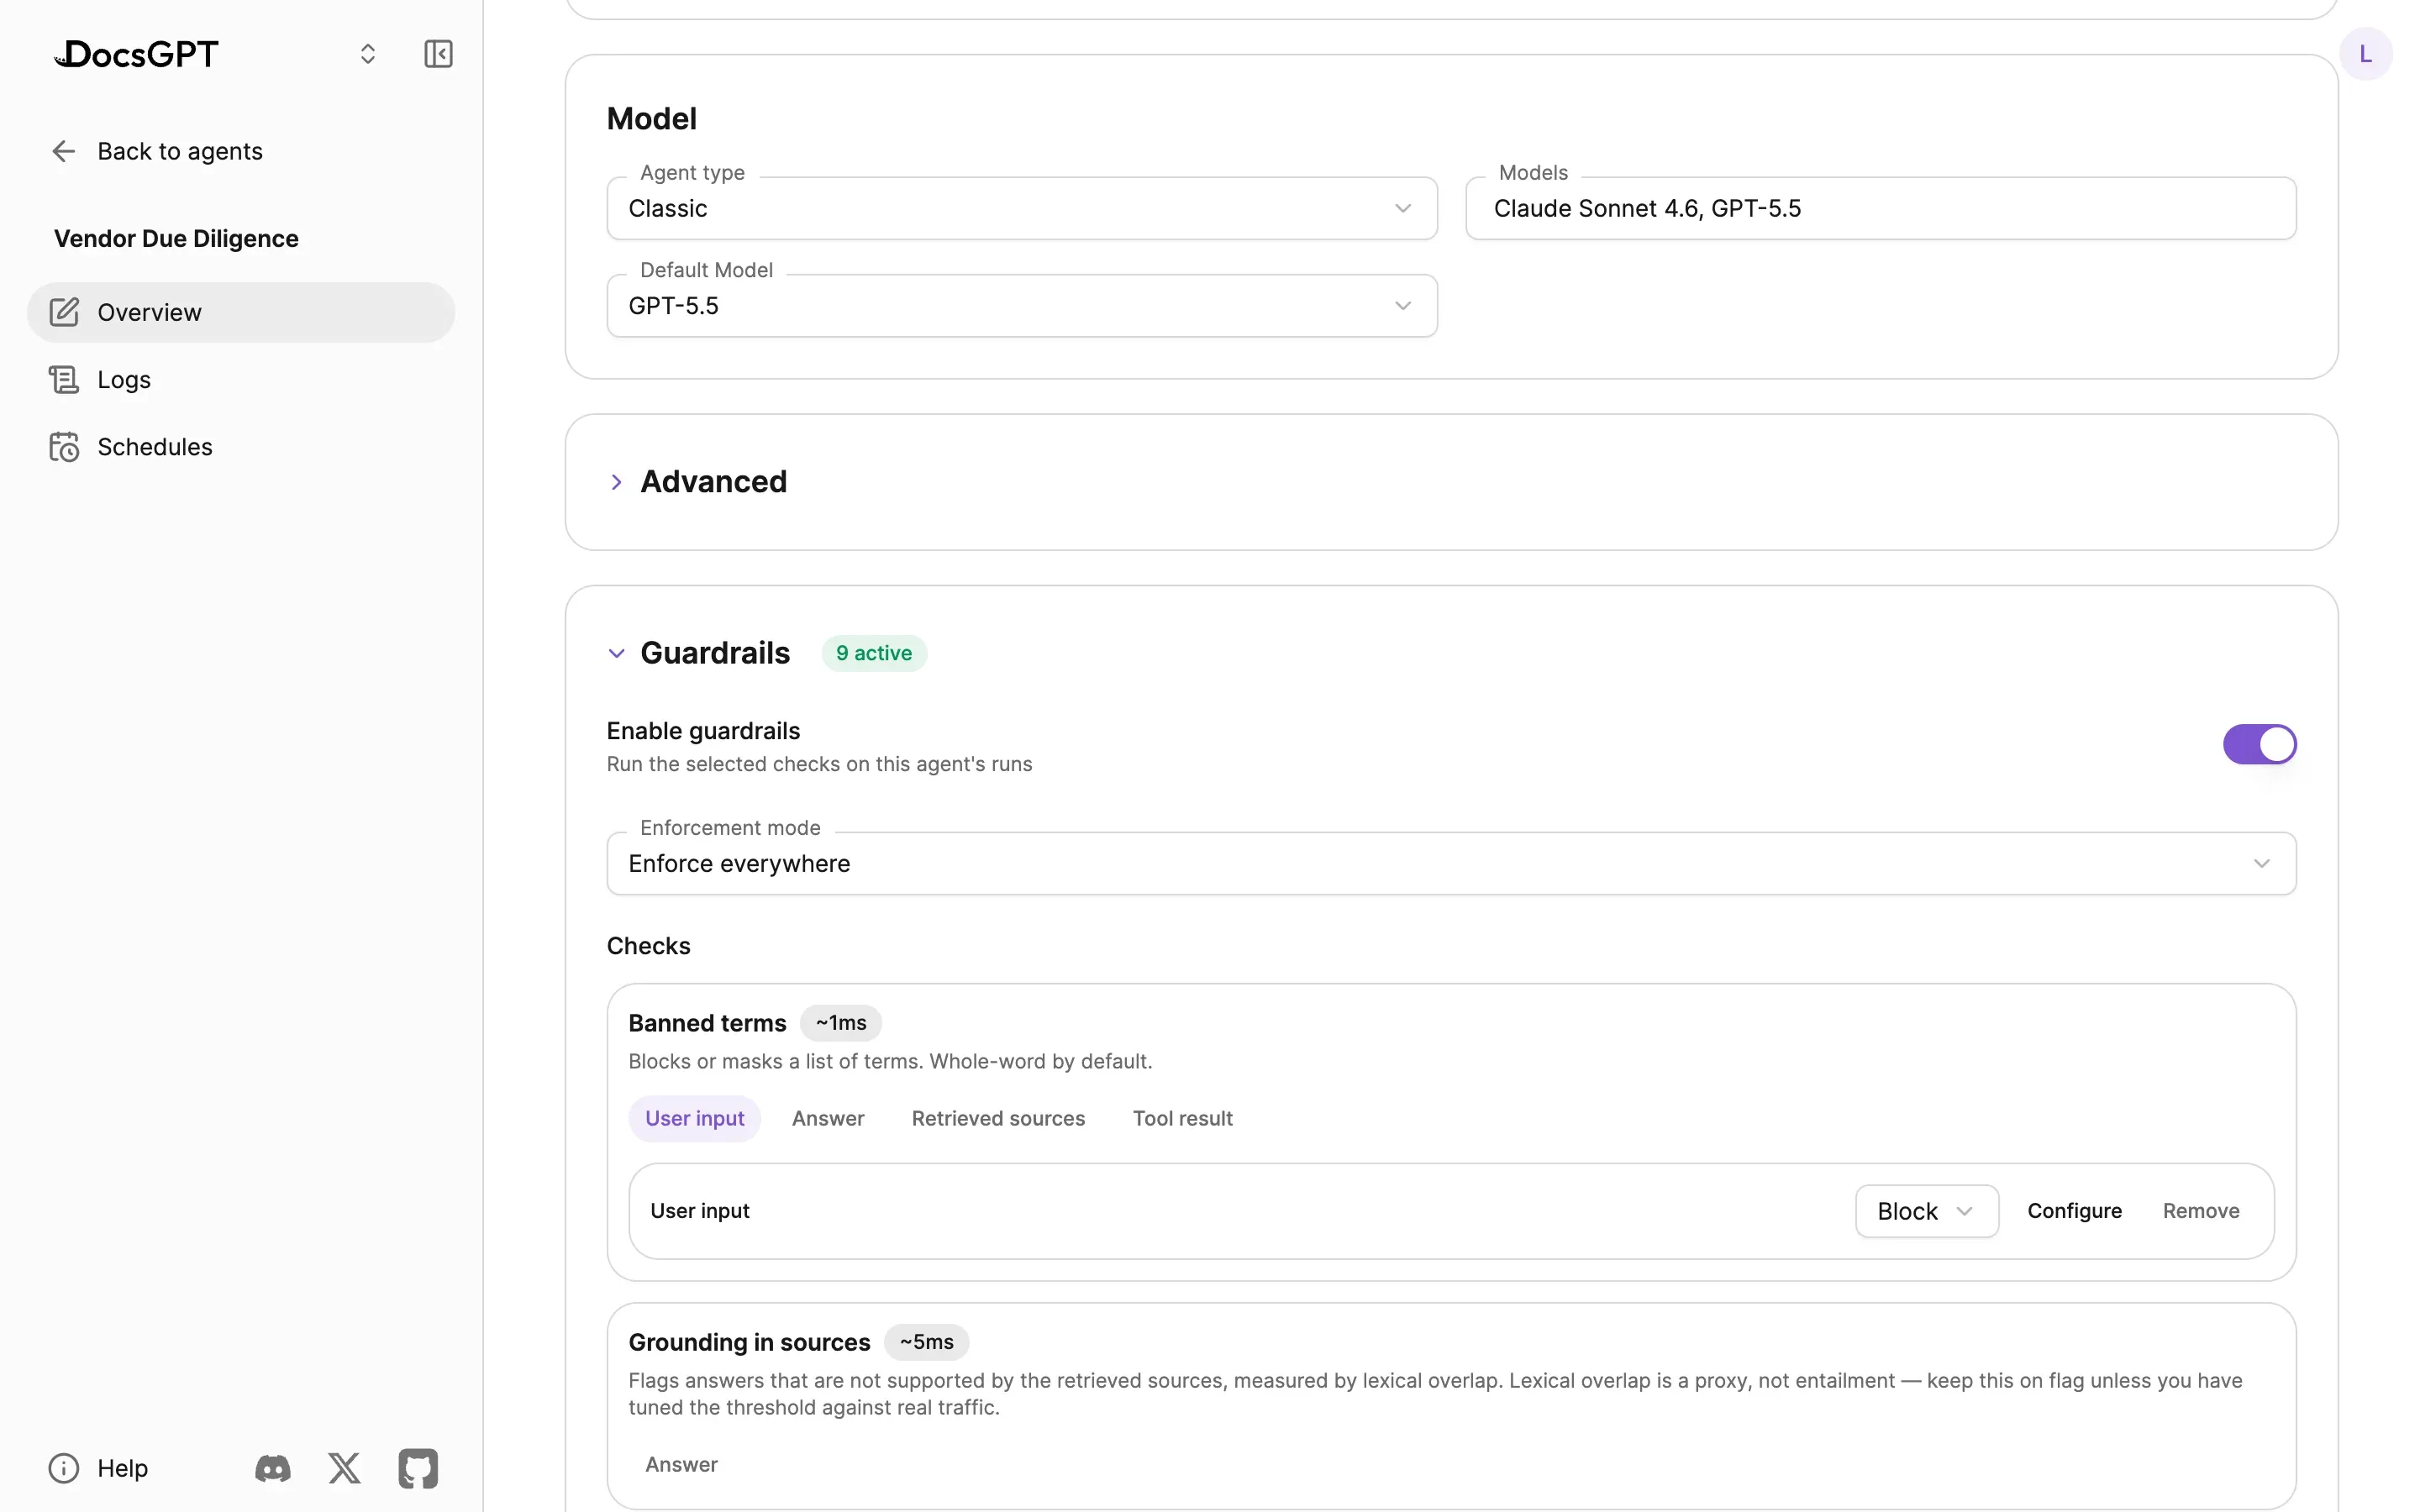
Guardrails run at four intervention points: user input, retrieved sources, tool results and the final answer. Seven built-in checks cover PII, credentials and secrets, banned terms, link policy, prompt-injection heuristics, grounding in retrieved sources and LLM-judge custom policies. Each check can flag, redact or block; each agent runs in monitor-only or enforce mode and chooses to fail open or closed, and an instance floor sets the minimum every agent inherits. Human approval can be required for chat responses and for tool calls, and every decision shows in Guardrail activity.
DocsGPT authenticates against any spec-compliant OIDC identity provider using Authorization Code with PKCE; Okta, Keycloak, Authentik and Entra ID are documented. Group allowlists and admin-group mapping control who gets in and who administers; Back-Channel Logout ends sessions when the IdP does. SCIM 2.0 provisions and deprovisions users with immediate session revocation.
Any spec-compliant IdP; Okta, Keycloak, Authentik and Entra ID documented. Authorization Code + PKCE; Back-Channel Logout.
group allowlists · admin group mapping
User lifecycle from the IdP with immediate session revocation on deprovisioning.
create · update · deactivate → sessions revoked
Global user and admin roles resolved server-side, never trusted from the client.
user · admin
Viewer / Editor sharing of agents, sources, prompts and tools. A shared tool runs with its owner's account or each person's own, and its secrets are never shown to others.
viewer · editor · your account · each person's own
Personal access tokens carry scopes, optional resource limits and an expiry; a forced logout revokes them with the sessions.
scopes · expiry · revocable
Admins choose which connectors are enabled, how shared tools sign in and whether they may write. Credentials are encrypted and bound to the person who connected them.
admin › connectors · write access
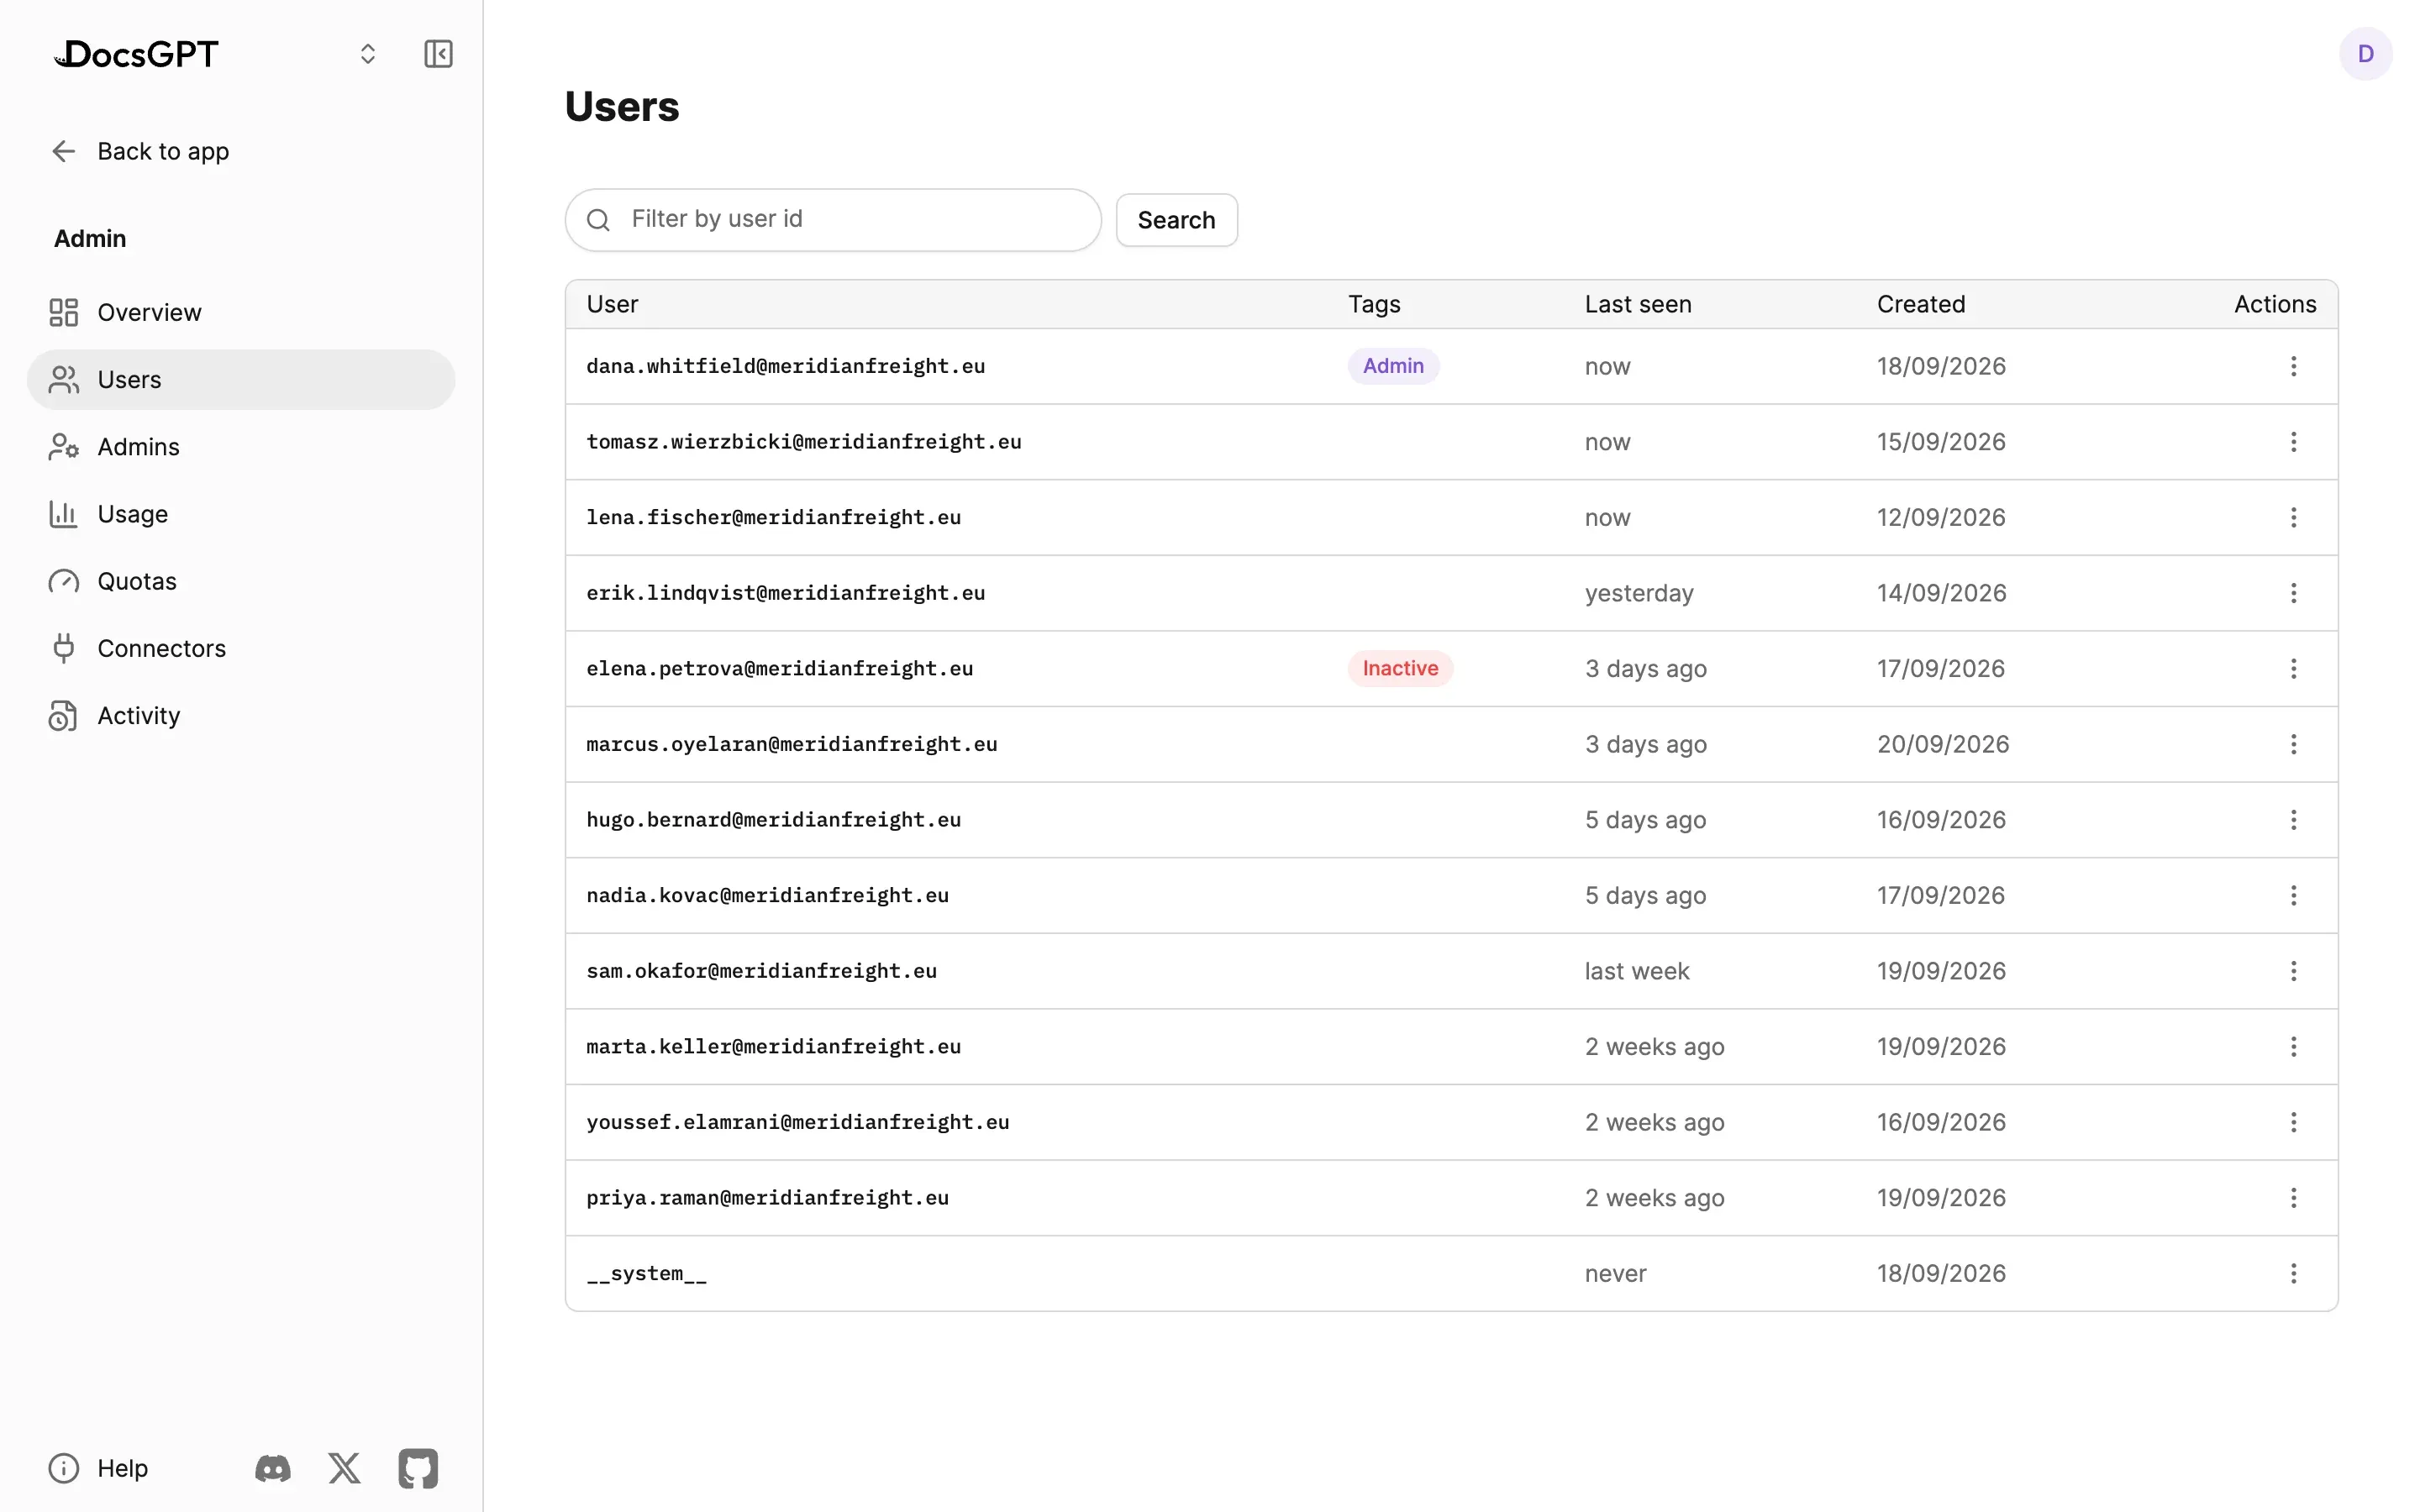
Admin › Activity is the audit log: sign-ins and denials, SCIM lifecycle, role and account changes, access tokens, quotas, connector policy, remote-device actions and guardrail decisions in one append-only feed. Filter it by person or category and export it as CSV or NDJSON for your SIEM. Usage shows tokens and cost by model, agent or flow, and the execution trace of every run exports over OpenTelemetry to the observability stack you already use.
Identity, access, configuration, data, device and safety events, each with who acted and on what.
append-only · actor · target
CSV or NDJSON, filtered first, ready for your SIEM.
csv · ndjson
Every block, redaction and flag with the check that fired; it records what matched, not the text.
blocked · redacted · flagged
Tokens and cost by model, agent or flow; run traces over OpenTelemetry to Langfuse, Datadog or Grafana.
OTel GenAI · langfuse · datadog · grafana
Code runs in a sandbox: a runner you host yourself, or Daytona. Secrets are stripped from its environment, its network can be locked down with the egress policy, and each runner is one trust domain, so teams that must stay apart get their own. Custom model, MCP and API endpoints reach public hosts only. Artifact bytes never pass through the model. The remote-device tool has approval modes, a denylist, and logs every action to Activity.
Self-hosted runner or Daytona; secrets stripped from the environment; about a minute per run.
self-hosted runner · daytona
The egress policy (a Kubernetes NetworkPolicy) locks the sandbox's network down; custom endpoints reach public hosts only.
egress policy · public hosts only
Generated DOCX, PPTX, XLSX and PDF bytes never pass through the model.
docx · pptx · xlsx · pdf
Approval modes and a denylist for actions on remote devices, each logged in Activity.
approve · deny · activity
quarterly-report.docx
artifact · append-only versions
Documentation
Two layers: what the application encrypts, and what the platform underneath provides.
Application layer · all postures
aes-gcm · your key · rotation · device tokens
Platform layer · On-premises, Air-gapped
For On-premises and Air-gapped deployments, disk and database encryption at rest and TLS in transit are provided by your platform, under your keys.
your disks · your database · your TLS · your keys
Platform layer · Cloud, Managed
For Cloud, the database, including vector embeddings, is encrypted at rest with AES-256 by the database provider, object storage uses server-side encryption, and TLS 1.2 or later carries traffic to the edge and on to every sub-processor. Managed instances inherit the same from their hosting provider.
AES-256 at rest · TLS 1.2+ in transit
DocsGPT is a GitHub Secure Open Source Fund participant (2026-08). The threat model is public (STRIDE), a software bill of materials is published, and CI runs CodeQL, Bandit and zizmor alongside Dependabot and secret scanning. Vulnerabilities are reported privately through SECURITY.md and handled under an incident-response playbook.
Programme
Participant since 2026-08.
2026-08 · participant
Threat model
Public STRIDE threat model for the platform.
STRIDE
SBOM
Exportable in SPDX format from the repository's GitHub dependency graph.
spdx · dependency graph
Dependencies
Automated dependency updates and alerts.
dependabot.yml
Static analysis
Code, Python and GitHub Actions workflow scanning in CI.
codeql · bandit · zizmor
Secrets
Repository secret scanning with push protection.
push protection
Disclosure
Private vulnerability reporting via GitHub.
private reporting
Response
Severity scale, triage, fix, release and advisory steps.
triage → fix → advisory
Files in the repository
GitHub stars
18,317
Contributors
239+
on GitHub
Licence
MIT
Applies to Cloud and Managed only. On-premises and Air-gapped deployments have no Arc53 sub-processors: nothing leaves your network. On Cloud, sub-processors fall into two groups: core infrastructure, which handles data whenever the service is used, and model and tool providers, which receive it only when a user or agent selects that model or tool. Each one, with its region and transfer mechanism, is listed in Annex III of the Data Processing Addendum, and changes are notified at least 15 days before they take effect. A Managed instance is provisioned for one customer, so its sub-processors and their regions are agreed with that customer rather than published here.
Report vulnerabilities privately through GitHub's private vulnerability reporting or to security@arc53.com, as described in SECURITY.md; the handling process is the public incident response plan. Security patches target the latest release and the main branch, so run the current release. Do not open a public issue and do not use the contact form.
Report privately
Use GitHub private vulnerability reporting on the DocsGPT repository, per SECURITY.md.
github.com/arc53/DocsGPT/security
Acknowledgement
Arc53 aims to acknowledge reports within 48 hours and validates the issue against the latest release and main.
48 h · security@arc53.com
Fix and release
Critical and High: fixed in a patched release with disclosure coordinated with the reporter, goal within 90 days. Medium and Low: included in the next scheduled release unless the risk requires an out-of-band patch.
critical/high ≤ 90 days · medium/low next release
Also patched
The managed cloud deployment is patched as soon as the fix is validated.
app.docsgpt.cloud
Coordinated disclosure
The advisory is published on GitHub once a fixed version is available, with affected and fixed versions.
Credit
Reporters are credited in the advisory unless they ask not to be.
DocsGPT publishes security advisories on GitHub. Eleven advisories have been published to date; each has been fixed in a released version. Details are as published on the GitHub advisories page.
| Severity | Affected versions | Fixed version | Published | |
|---|---|---|---|---|
| GHSA-q463-hvr7-49m3 | Critical | < 0.19.0 | 0.19.0 | 2026-10-04 |
| GHSA-46rm-v974-c7gw | Critical | < 0.19.0 | 0.19.0 | 2026-10-04 |
| GHSA-73g6-pg2w-xvpf | High | < 0.19.0 | 0.19.0 | 2026-10-04 |
| GHSA-2q66-89mh-pjfr | High | < 0.19.0 | 0.19.0 | 2026-10-04 |
| GHSA-pjj3-xfwm-h5fq | High | < 0.17.2 | 0.17.2 | 2026-10-04 |
| GHSA-949x-3mqg-5xfr | Medium | < 0.21.0 | 0.21.0 | 2026-10-04 |
| GHSA-666p-752v-j875 | Medium | < 0.19.0 | 0.19.0 | 2026-10-04 |
| GHSA-gcrq-f296-2j74 · CVE-2026-26015 | Critical | ≥ 0.15.0, < 0.16.0 | 0.16.0 | 2026-04-28 |
| GHSA-m448-vp23-j393 | High | < 0.15.0 | 0.15.0 (advisory gives the affected range only) | 2026-06-07 |
| GHSA-6gxj-6hq5-hqcj | Medium | All versions before commit 249dd9c | Commit 249dd9c; in 0.17.0 and later | 2026-06-07 |
| GHSA-p5qc-vj2x-9rjp · CVE-2024-31451 | Low | 0.5.0 | 0.8.1 | 2024-04-12 |
As published on GitHub, checked 2026-10-04.
If you run DocsGPT, run the current release (v1.0.0): the upgrading guide has the steps and the changelog what changed.
DocsGPT does not hold a SOC 2, ISO 27001 or Cyber Essentials certificate today. The evidence for a security questionnaire is the posture you choose plus the programme above: a public threat model, SBOM, CodeQL and dependency scanning, coordinated disclosure and an inspectable MIT codebase.
GDPR compliance is the deploying organisation's responsibility; DocsGPT supplies the controls. Keep personal data inside your jurisdiction by running on-premises, in the EU region on Cloud or in a chosen Managed region, sign a DPA, log every access, delete on request and redact PII before it reaches a model.
Air-gapped and On-premises keep documents, prompts and embeddings inside your network; nothing is sent to Arc53.
on-premises · air-gapped
The EU region on Cloud; the Americas, Europe, Middle East, Africa or Asia on Managed, chosen at provisioning; or your own data centre.
EU (cloud) · 5 regions (managed) · your DC
The Data Processing Addendum for Cloud and Managed, with its processing details, security measures and sub-processor annex, at /dpa.
/dpa
An append-only, exportable audit log. You delete sources and conversations, admins deactivate users, and erasing a person's records entirely is done in the database on your own deployment, or on request on Cloud and Managed.
activity · delete · deactivate
Flag, redact or block PII on input, retrieved sources and answers.
pii · redact
The standard questionnaire questions, each linked to its answer.
| Answer | |
|---|---|
| Where is our data stored and processed? | Posture table · Cloud, Managed, On-premises, Air-gapped |
| Is our data used to train models? | No, on any posture · Posture table |
| Does any data leave our network? | Posture table (air-gapped definition) · Air-gapped deployment |
| Which IdPs are supported; is SCIM available? | Identity · docs OIDC SSO, SCIM |
| Is there an audit trail and can we export it? | Audit log (CSV, NDJSON) · docs Activity, Traces |
| Is there a hardening checklist for self-hosting? | docs Security checklist |
| Can the LLM execute code or call tools safely? | Sandboxing · docs Sandbox, Tools |
| Are prompts/answers checked for PII or injection? | Guardrails · docs Guardrails |
| Encryption at rest and in transit? | Encryption |
| Sub-processors and DPA? | Cloud sub-processors · DPA |
| How are vulnerabilities reported and fixed? | Vulnerability disclosure · Advisories · SECURITY.md |
| Certifications held? | Certifications |
| Licence and source availability? | GitHub repository · MIT |
| Uptime commitment, backups and recovery? | Posture table (99.9 % uptime on Cloud and Managed; daily backups, point-in-time recovery) · Pricing |
| Business continuity / key-person risk? | MIT core, open-format export, documentation · Pricing FAQ |
A 30-minute demo, or a free on-premises review of your hardware, identity and network posture with an Arc53 engineer.